Why RaspAP?
Building an access point on a Pi by hand means configuring hostapd (the Wi-Fi side), dnsmasq (DHCP and DNS) and iptables (NAT) separately. Each has its own config format, and all three have to agree with each other. RaspAP sets them up from a known-good default configuration and gives you a web UI for changing settings later, so you don't have to SSH in for every change.
According to the RaspAP documentation, it offers:
- A web dashboard for hotspot, DHCP and DNS settings
- OpenVPN and WireGuard client support
- DNS-based ad blocking, including custom blocklists
- Data usage graphs through vnStat
- Captive portal support through Nodogsplash (the FAQ links a plugin that installs it)
Requirements
- A Raspberry Pi with onboard wireless. RaspAP's images and installer target all current Pi models with onboard Wi-Fi. If you haven't set up a Pi before, start with the Raspberry Pi Setup Guide.
- A clean install of Raspberry Pi OS Lite based on Debian 13 "trixie" or Debian 12 "bookworm", 32- or 64-bit. The docs' compatibility table lists these as officially supported. The FAQ traces many odd problems to installing on a system that wasn't clean.
- A microSD card of at least 8 GB (the FAQ's recommendation for RaspAP) from a reputable manufacturer.
- The official power supply for your model. The setup docs note that inadequate voltage causes many Wi-Fi problems.
- An Ethernet connection for the initial setup, so you aren't reconfiguring Wi-Fi over Wi-Fi.
- Optional: a USB Wi-Fi adapter with in-kernel drivers, if the Pi should join an upstream Wi-Fi network and broadcast its own at the same time.
Versions: this guide follows RaspAP's current documentation. RaspAP added support for Debian 13 trixie, and its prebuilt images are based on Raspberry Pi OS Lite (trixie). Check the compatibility table on the docs home page before installing on any other distribution.
Installation
Option 1: Raspberry Pi Imager
The simple setup guide calls this the easiest route. In Raspberry Pi Imager choose OS → Other specific-purpose OS → RaspAP, pick 64-bit or 32-bit, and use the customisation settings before writing the card:
- Create a user. RaspAP's images don't preconfigure one, and a headless boot stalls at an interactive prompt if no user is defined.
- Enable SSH if you'll run the Pi without a screen.
- Don't add your home Wi-Fi network. The FAQ lists Imager's preconfigured wireless settings as one cause of an access point that behaves unpredictably.
These images preset the Wi-Fi country to US so that rfkill doesn't block the radio. If you're elsewhere, change it on first boot with sudo raspi-config under Localisation Options.
Option 2: Quick installer on Raspberry Pi OS
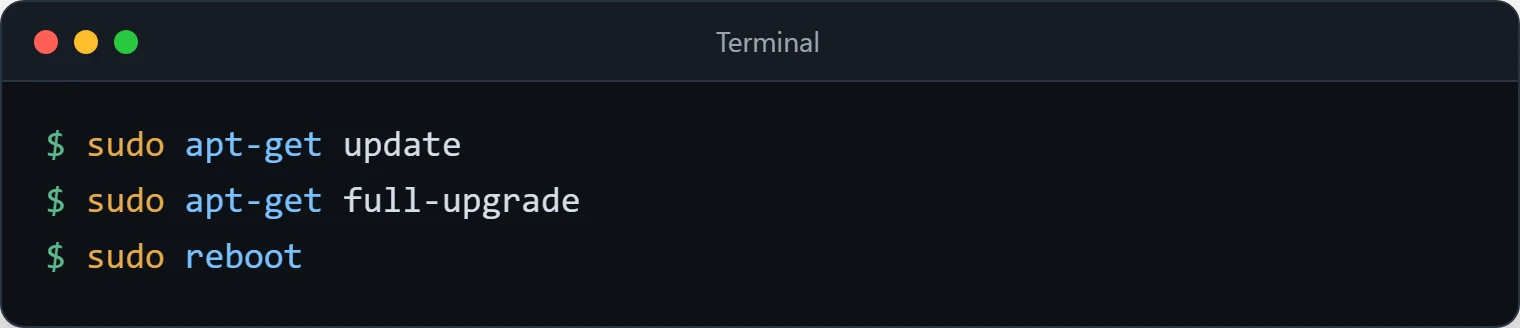
Start from a fresh Raspberry Pi OS Lite install and bring it up to date, including the kernel and firmware:
sudo apt-get update
sudo apt-get full-upgrade
sudo reboot
Set the Wi-Fi country with sudo raspi-config (Localisation Options). The docs warn that without it the Pi won't enable wireless and you'll see "Wi-Fi is currently blocked by rfkill" in the console. Then run the quick installer:
curl -sL https://install.raspap.com | bashThis downloads and runs RaspAP's install script. To read its options before running it, use curl -sL https://install.raspap.com | bash -s -- --help.
The installer asks about optional components such as ad blocking, OpenVPN, WireGuard, the REST API and VPN provider integration. Only install what you'll use: ad blocking makes little sense if Pi-hole or AdGuard Home already filters this network, OpenVPN is for VPN services that hand out .ovpn files, and WireGuard is for a WireGuard server you can connect to. For an unattended install, the same choices can be passed as flags, for example curl -sL https://install.raspap.com | bash -s -- --yes --wireguard 1 --adblock 0. Accept the reboot at the end.
Default Settings
After the reboot, RaspAP broadcasts a routed access point with these defaults, taken from the access point and authentication docs:
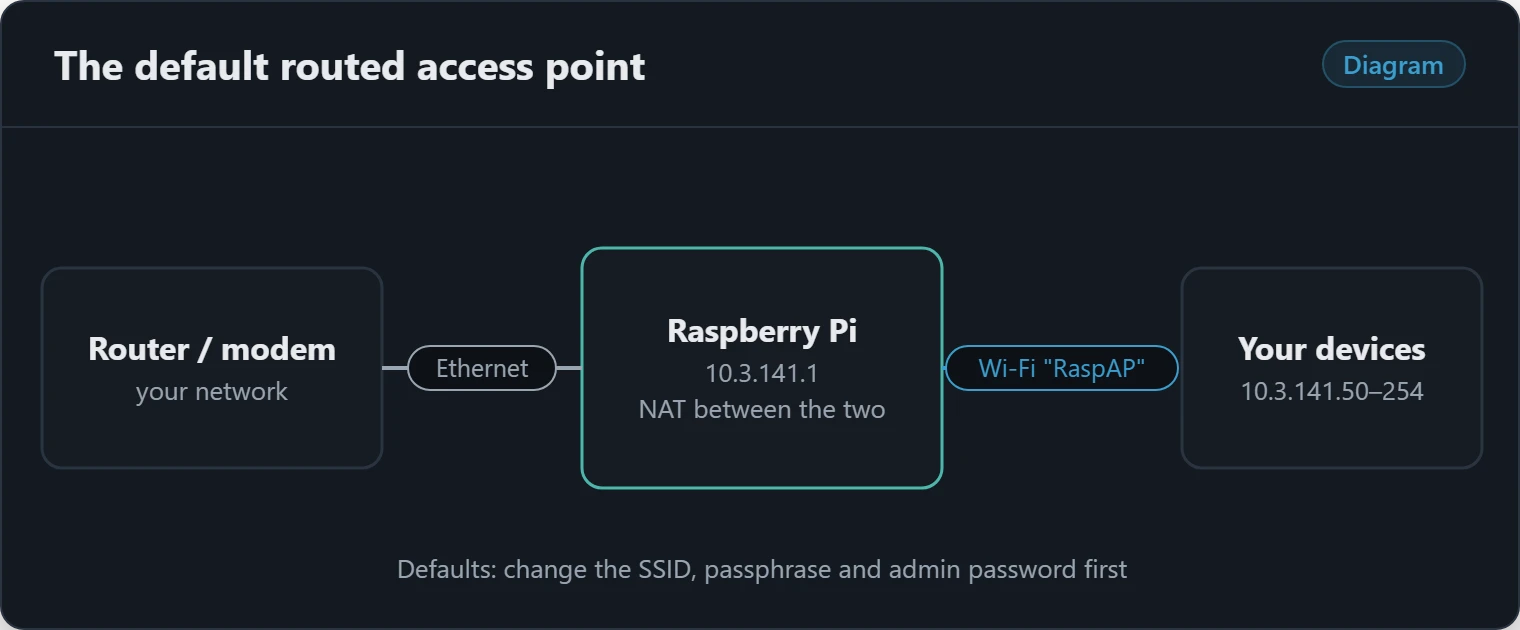
- SSID: RaspAP
- Passphrase: ChangeMe (WPA2 with CCMP, 2.4 GHz, channel 1)
- Web interface:
http://10.3.141.1 - Admin login:
admin/secret - DHCP range for clients: 10.3.141.50 to 10.3.141.254
Change the admin password, the SSID and the passphrase before anything else. RaspAP's docs advise assuming that these defaults are known to everyone, and anyone who joins the access point can reach the login page. Note also that the login is sent in plain text over HTTP; the quick installer's --cert option sets up a locally trusted certificate so the web UI can use HTTPS.
Basic Configuration
Hotspot settings
On Hotspot → Basic, set a unique SSID, the wireless mode and the channel. In the 2.4 GHz band, channels 1, 6 and 11 don't overlap, so pick whichever of them your neighbours use least. For 5 GHz, first select your country on Hotspot → Advanced, then choose the 802.11ac mode on the Basic tab; RaspAP lists only the channels permitted for that country. Choose Save settings, then Restart hotspot.
On Hotspot → Security, keep WPA2 with CCMP and set a passphrase of 8 to 63 printable ASCII characters (the magic icon next to the field generates one). WPA3 is marked experimental, and the docs note the Pi's onboard Wi-Fi doesn't support it, so it needs an external adapter.
Admin password
Change it on Authentication → Basic. If you forget it later, sudo rm /etc/raspap/raspap.auth restores the default login, which you should then change again.
Internet source
By default RaspAP runs a routed access point: wlan0 broadcasts the network at 10.3.141.1/24, and client traffic is translated (NAT) out through the Pi's other connection, usually Ethernet. If routing and NAT are unfamiliar, Networking Fundamentals explains them.
- Ethernet to Wi-Fi (the default): plug the Pi into your router or modem; the onboard radio broadcasts the access point.
- Wi-Fi to Wi-Fi: one radio joins the upstream network and another broadcasts yours. With a second adapter connected, RaspAP detects it (for example as
wlan1) and uses it as the client interface. Running both roles on one radio (AP-STA mode) exists, but the docs mark it experimental and unsupported. - Bridged AP mode (Hotspot → Advanced) hands DHCP to your main router instead. After switching, the web UI is no longer at 10.3.141.1.
For USB adapters, the FAQ recommends models with in-kernel Linux drivers and links a community list of adapters that work without installing extra drivers.
WiFi Client Mode
To join an upstream Wi-Fi network from the dashboard, open the WiFi client page, scan, pick the network, enter its passphrase and connect. Devices on your access point then reach the internet through that network, and they all sit behind the Pi.
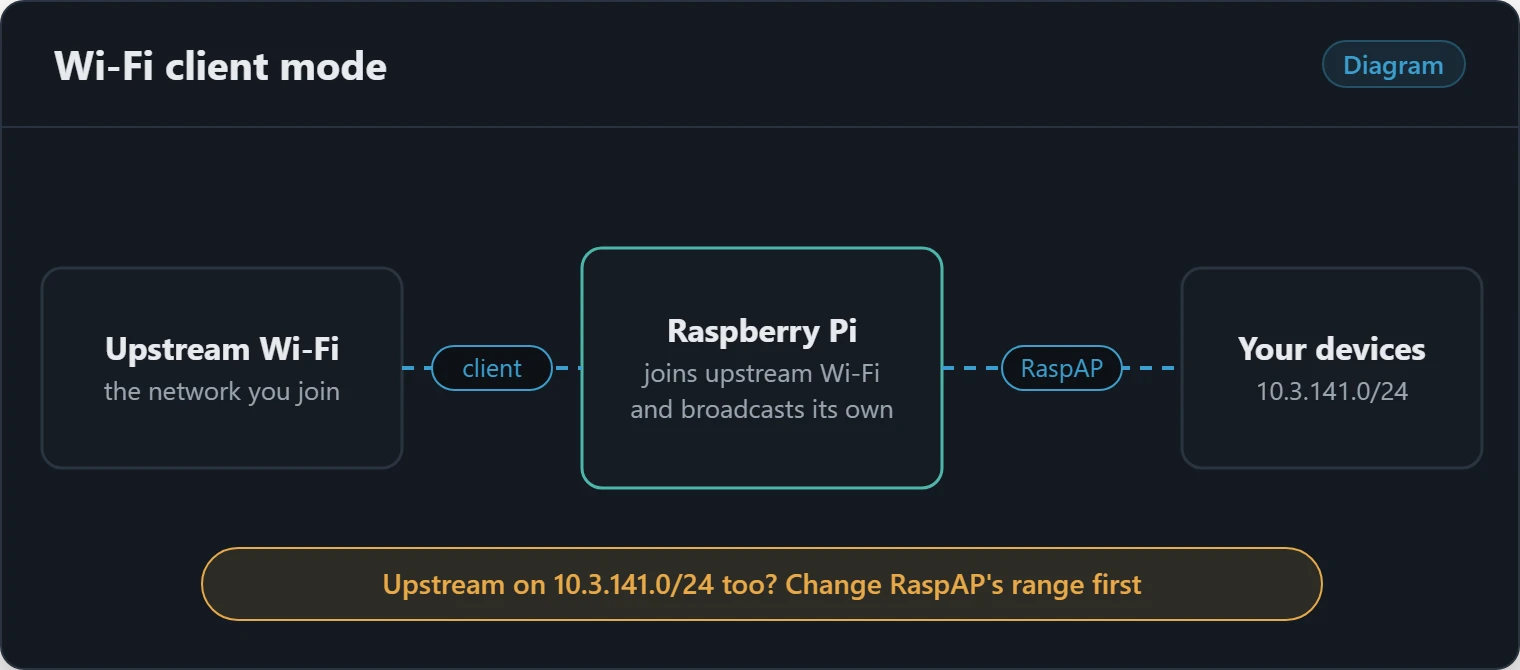
One thing to check: RaspAP's own network is 10.3.141.0/24. If the upstream network uses the same range, routing breaks in confusing ways. Change RaspAP's address and DHCP range in the DHCP server settings to a range the upstream network doesn't use before you connect.
VPN Integration
Running the VPN on the access point means every connected device uses the tunnel, without a VPN app on each one.
OpenVPN
RaspAP can store several OpenVPN client profiles: upload a .ovpn file with its login credentials, then activate the profile you want. If you run your own server, OpenVPN Cloud Deployment covers that side.
WireGuard
On the WireGuard page, select Upload file under Configuration Method, choose a valid WireGuard config and save. The FAQ points out that RaspAP is only a front end and can't validate the config itself, so build and test it first; WireGuard Cloud Deployment shows how to create the server and client configs. For debugging, enable the debug log on the WireGuard logging tab, or run sudo journalctl --identifier wg-quick.
The installer can also integrate a few commercial VPN providers' Linux clients, which the defaults page describes as beta support.
Ad Blocking
If you installed it, ad blocking works through dnsmasq blocklists, and the FAQ says custom blocklists are supported. It runs on the same Pi with no extra software.
If you already run Pi-hole on another device, use it as RaspAP's upstream instead: on DHCP Server → Advanced, enable the Upstream DNS Server option, enter the Pi-hole's address, save and restart dnsmasq. Both projects use dnsmasq, so putting them on the same Pi is harder; the FAQ's options are running Pi-hole in Docker or, for AdGuard Home, moving it to port 5300 on 127.0.0.1 and adding 127.0.0.1#5300 as RaspAP's upstream. See AdGuard Home Deployment for that setup.
Captive Portal
For a guest network with a splash page, the FAQ recommends Nodogsplash, which works with RaspAP, and links a plugin that installs it. Keep the landing page short: the terms, the network name and a button to continue.
Performance Notes
The FAQ explains the main limits:
- The Pi's onboard Wi-Fi chip connects to the processor over a narrow SDIO link, so throughput stays well below the radio's headline rate.
- On 2.4 GHz, an 802.11n access point falls back to 20 MHz channels when other networks are nearby, which roughly halves its maximum throughput. The 5 GHz band has more non-overlapping channels and usually less interference.
- Metal cases reduce wireless range noticeably. If the SSID appears and disappears, try without the case and on a less crowded channel.
- Undervoltage causes disconnects. Check the kernel log with
dmesg | grep -i voltage, and use the official power supply.
Keep the Pi focused on routing: other heavy services on the same board compete for CPU and memory.
Travel Router Setup
A small Pi with RaspAP can act as a travel router: your devices stay connected to your own SSID, and only the Pi joins the hotel or conference network. A typical kit:
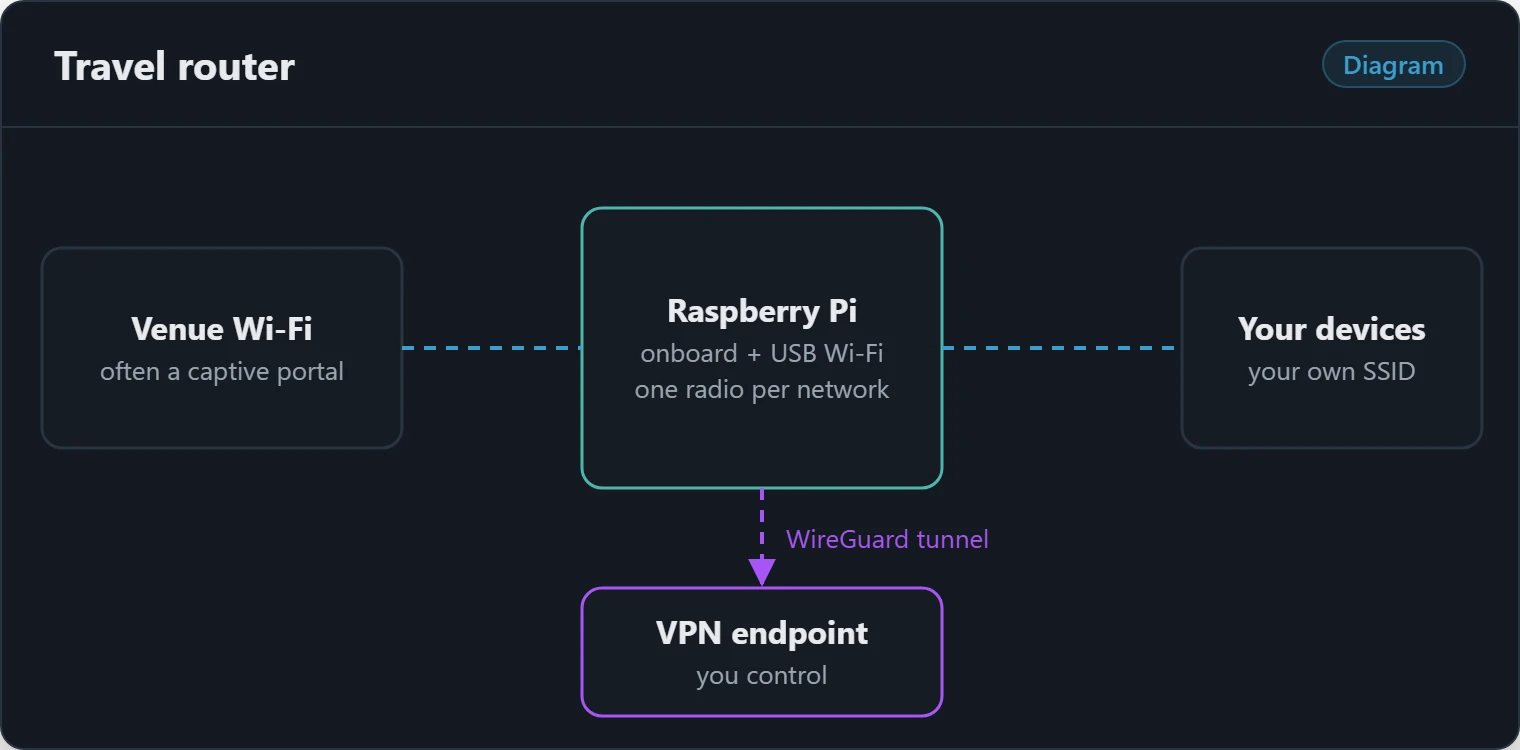
- A Pi with onboard Wi-Fi plus a USB Wi-Fi adapter, so one radio joins the venue's network and the other serves yours
- A USB power supply or power bank that meets the model's power requirements
- A WireGuard client config that points to a VPN endpoint you control
Many venue networks use a captive portal. Complete that login from a device on your RaspAP network before you enable the VPN, because the tunnel can't connect until the venue's network lets traffic through. To reduce SD card wear on a device you carry around, the quick installer's --minwrite option configures RaspAP's minimal write mode.
Troubleshooting
The access point doesn't appear
- Wi-Fi blocked by rfkill. If you see "Wi-Fi is currently blocked by rfkill", the Wi-Fi country isn't set.
rfkill listshows whether the radio is soft-blocked. Set the country withsudo raspi-config(Localisation Options) and reboot. - hostapd isn't running. Check
sudo systemctl status hostapd. For details, turn on the logfile output on Hotspot → Logging, save, restart the hotspot and read the log. - Unsupported 5 GHz channel. A log line saying the hardware doesn't support the configured channel means you should pick another one; the FAQ suggests 36, 40, 44 or 48.
- Nothing after a reboot. RaspAP's
raspapd.servicestarts the network services in order; check it withsudo systemctl status raspapd.service.
Clients connect but get no IP address
- Forget the network on the client and reconnect, then try Restart hotspot in RaspAP.
- Enable Log DHCP requests on DHCP Server → Logging. A working lease shows four steps: DHCPDISCOVER, DHCPOFFER, DHCPREQUEST and DHCPACK. Where the sequence stops tells you whether the client or the server side is failing.
- Check the DHCP server itself with
sudo systemctl status dnsmasq. - If you added firewall rules (ufw or iptables), make sure they allow DNS (port 53) and DHCP (UDP port 67) on the access point interface.
- As a last resort, give the device a static lease on DHCP Server → Static Leases.
Clients have an address but no internet
- Check the upstream link:
ip routeon the Pi should show a default route through Ethernet or the client Wi-Fi interface. - Check NAT:
sudo iptables -t nat -L -n -vshould list a MASQUERADE rule in the POSTROUTING chain. - From the Pi,
ping -c 3 1.1.1.1tests the connection andnslookup example.comtests DNS. - If Docker is installed on the same Pi, read the FAQ entry on running Docker alongside RaspAP, which explains what breaks and how to fix it.
The web interface won't load
- Type
http://10.3.141.1; a browser that forceshttps://produces misleading errors unless you enabled HTTPS. - If the access point itself is down, connect by Ethernet and reach the Pi on its wired address over the browser or SSH.
Updating or Removing RaspAP
The quick installer also handles maintenance. curl -sL https://install.raspap.com | bash -s -- --version prints the latest release, --update performs a minimal update that keeps your configuration files, and --uninstall runs the uninstaller. Connect over Ethernet first: both change the services that run the access point, so Wi-Fi clients, and you if you're on Wi-Fi, drop off while it runs.
Next Steps
- Set up a WireGuard server at home or on a VPS (WireGuard Cloud Deployment) and point the Pi's tunnel at it, so traffic from any network goes through a connection you control.
- For more control over DNS filtering than RaspAP's built-in blocker, run Pi-hole on a separate device and set it as RaspAP's upstream DNS server.
- Read the RaspAP FAQ; it covers many edge cases, including bridged mode and multiple adapters.