Why Pritunl instead of plain OpenVPN
A hand-built OpenVPN server (see OpenVPN Cloud Deployment) means running Easy-RSA commands every time someone joins or leaves. Pritunl does that bookkeeping in a web console: you add a user, it issues the certificate and builds the profile, and disabling the user cuts off access. The trade-off is two more services to keep patched and backed up, the Pritunl web server and MongoDB.
Decide these before you install
- Distribution. Pritunl's installation page says all development and testing are done on Oracle Linux and recommends it, with AlmaLinux as the alternative when Oracle Linux isn't available; both have full support for Pritunl's SELinux profiles. Ubuntu 24.04 is documented too, but the same page says future Ubuntu support isn't tested or guaranteed. This guide uses the Ubuntu 24.04 commands; the Oracle Linux and AlmaLinux commands are on the same page, and the rest of the guide applies to both.
- Memory. A single server runs MongoDB next to Pritunl, and Pritunl recommends high-memory instances for the database. Check usage with
free -honce everything runs. - Ports. The web console listens on TCP 443, and a second web server on TCP 80 answers Let's Encrypt validation and redirects HTTP to HTTPS (configuration page). Each VPN server you create gets its own UDP port. If something else already uses 443, change the console port with
sudo pritunl set app.server_port PORT. - Firewall. Pritunl writes its own iptables rules, and its security guide says not to run UFW, firewalld or another software firewall on the server because they break its configuration. Filtering happens in an external firewall or the cloud provider's security group instead.
You also need a server with a public IP address (Launch Your First EC2 Instance walks through one provider), access to its browser or serial console, and optionally a DNS name pointing at it for a Let's Encrypt certificate.
Set up the cloud firewall first
Because the install turns off UFW, the provider's security group becomes the only filter in front of the server. Set it up before you install anything:
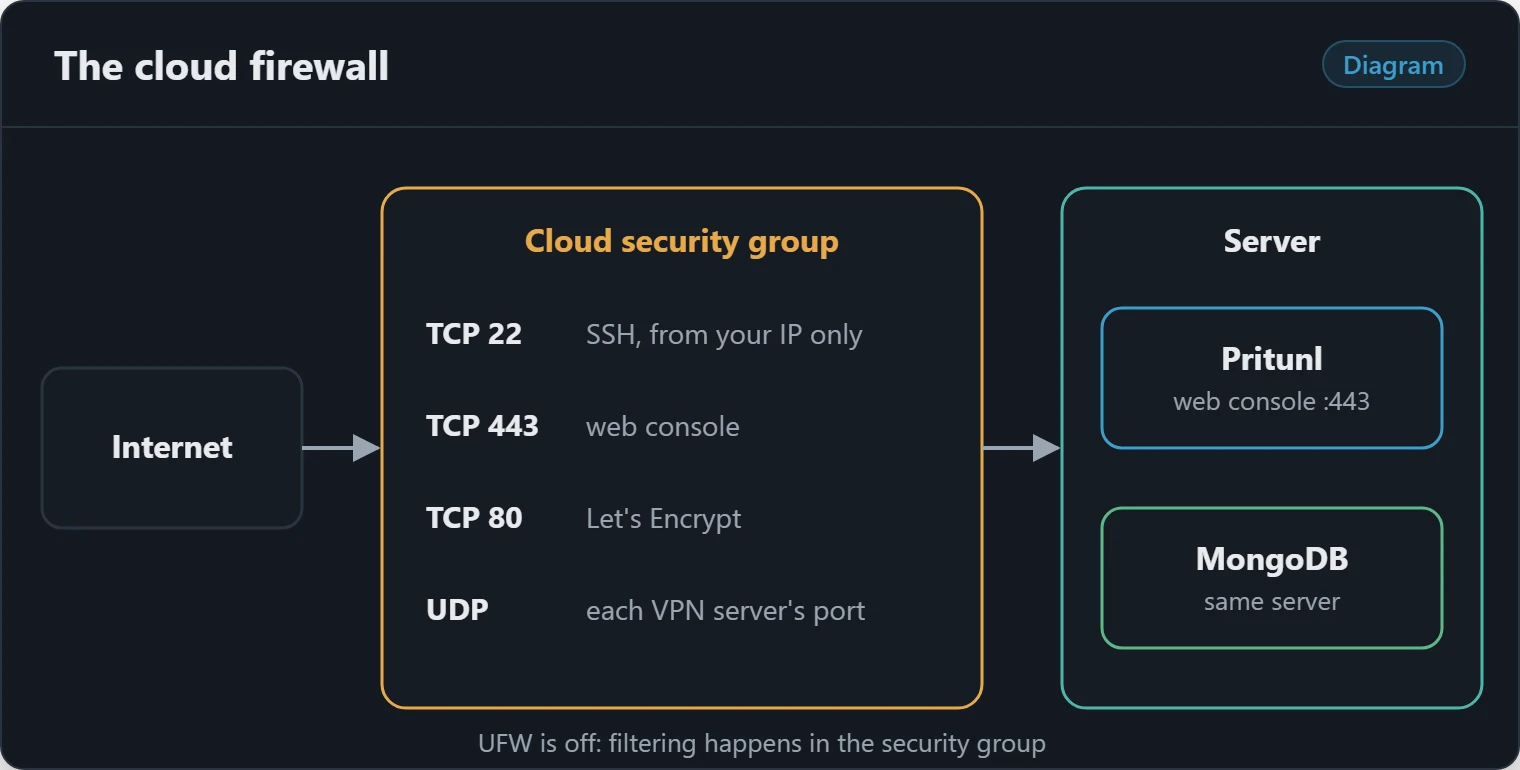
- TCP 22 (SSH) from your own IP address only.
- TCP 443 for the web console. Restrict it to your IP if only administrators use the console; users who download profiles through profile links need to reach it too.
- TCP 80 if you'll use a Let's Encrypt certificate. The configuration page says it must be publicly open for validation and renewals.
- The UDP port of each VPN server, which you'll add once Pritunl picks it.
Turning UFW off can't lock you out, but it does remove the VM's own filtering, which is why this comes first.
Installation (Ubuntu 24.04)
These commands are the Ubuntu 24.04 section of Pritunl's installation page as of October 2026. Repository lines change between releases (the MongoDB version and the Ubuntu codename in particular), so compare them with the official page before you run them.
Add Repositories
sudo tee /etc/apt/sources.list.d/mongodb-org.list << EOF
deb [ signed-by=/usr/share/keyrings/mongodb-server-8.0.gpg ] https://repo.mongodb.org/apt/ubuntu noble/mongodb-org/8.0 multiverse
EOF

sudo tee /etc/apt/sources.list.d/openvpn.list << EOF
deb [ signed-by=/usr/share/keyrings/openvpn-repo.gpg ] https://build.openvpn.net/debian/openvpn/stable noble main
EOF

sudo tee /etc/apt/sources.list.d/pritunl.list << EOF
deb [ signed-by=/usr/share/keyrings/pritunl.gpg ] https://repo.pritunl.com/stable/apt noble main
EOF

sudo apt --assume-yes install gnupg

curl -fsSL https://www.mongodb.org/static/pgp/server-8.0.asc | sudo gpg -o /usr/share/keyrings/mongodb-server-8.0.gpg --dearmor --yes
curl -fsSL https://swupdate.openvpn.net/repos/repo-public.gpg | sudo gpg -o /usr/share/keyrings/openvpn-repo.gpg --dearmor --yes
curl -fsSL https://raw.githubusercontent.com/pritunl/pgp/master/pritunl_repo_pub.asc | sudo gpg -o /usr/share/keyrings/pritunl.gpg --dearmor --yes
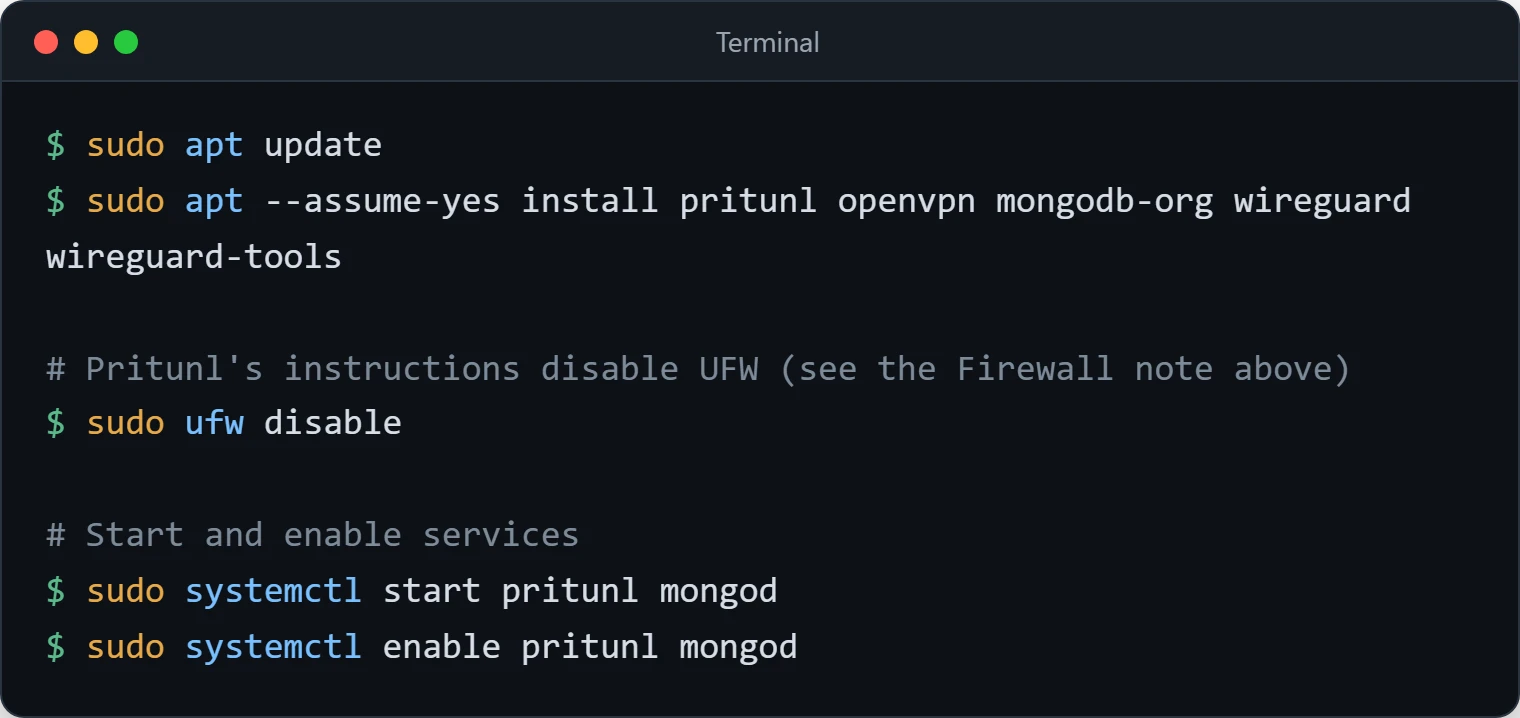
Install
sudo apt update
sudo apt --assume-yes install pritunl openvpn mongodb-org wireguard wireguard-tools

# Pritunl's instructions disable UFW (see the Firewall note above)
sudo ufw disable

# Start and enable services
sudo systemctl start pritunl mongod
sudo systemctl enable pritunl mongod
Check: both services are running and the web servers are listening:
systemctl is-active pritunl mongod
sudo ss -tlnp | grep -E ':(80|443) '
The first command prints active twice. If pritunl isn't listening on 443, look at sudo journalctl -u pritunl -b; another program holding the port is a common cause.
Initial Setup
Open https://YOUR_SERVER_IP in a browser. It warns about the self-signed certificate until you set up Let's Encrypt. The database setup screen asks for a setup key and the MongoDB URI. Get the key with:
sudo pritunl setup-keyLeave the MongoDB URI at its default when MongoDB runs on the same server.
The login dialog follows. The default username is pritunl; get the default password with:
sudo pritunl default-passwordThe initial setup dialog after login lets you change the username and password. Do it straight away; the steps are on Pritunl's configuration page.
Configure Settings
Settings (gear icon):
- Public Address - detected automatically; change it only if it's wrong
- Web Console Port - 443 by default
- Lets Encrypt Domain - a domain that points at the server, for a signed certificate on the console (port 80 must be reachable for validation)
Create Server and Organization
Organization
Click Add Organization in the web console. Organizations group users; create at least one.
Server
Servers → Add Server
- Name: Something descriptive
- Port: a random UDP port is selected by default
- Protocol: UDP by default; TCP can help on networks that block UDP
- Virtual Network: also random by default; it must not overlap the local networks your clients use, and must be large enough for every user attached to the server
- DNS Server: set to Google's public DNS by default
Click Attach Organization to attach your organization to the server.
Routes decide what goes through the tunnel. A new server includes 0.0.0.0/0, which sends all of a client's internet traffic through the VPN. Pritunl's security guide advises against that route on cloud and enterprise networks: with everything routed and NATed through the server, a VPN user can query the cloud metadata service at 169.254.169.254 or reach the MongoDB database if it isn't protected. To reach only one network, remove 0.0.0.0/0 and add a route for it, for example 192.168.0.0/24. The connecting guide covers these defaults.
Server settings the security guide recommends
Pritunl's security guide lists settings for servers that need tighter security. These are the ones that apply to a single-server setup:
- In the server's settings: Encryption Cipher AES 128bit GCM (the guide says 256-bit GCM is noticeably slower and supports fewer concurrent clients), Hash Algorithm SHA-256, DH Param Bits 2048 or 4096, and Restrict Routing enabled.
- In the top-right settings: enable Drop OpenVPN Permissions so the OpenVPN process doesn't run as root, and set Auditing Mode to All.
- Run the web server as its own non-root systemd service:
sudo pritunl set app.web_systemd true, thensudo systemctl restart pritunl.sudo systemctl status pritunl-webshould then show it active.
Add Users
Click Add User and choose the organization. An email address and a PIN are optional.
On the Users page, the download button gives you the user's profile. The profile links button creates temporary links to the profile in different formats, including a URI that the Pritunl Client can import directly.
Start Server
On the Servers page, select the server and click Start Server.
Allow the server's UDP port (shown on the server) in your security group or external firewall. On AWS, if clients need to reach other networks through the server, disable the instance's source/destination check in the EC2 network interface settings; Pritunl's configuration page describes this and the Google Cloud forwarding equivalent.
Check: the server shows as online in the console, and sudo ss -ulnp on the host lists an openvpn process on the server's port.
Client Connection
Import the profile into the Pritunl Client or any other OpenVPN client:
- Download the profile or open a profile link.
- Import it into the Pritunl Client, OpenVPN Connect or a similar client.
- Connect.
Check: the user shows as connected on the Users page, and the server's output in the console logs the connection. With the default 0.0.0.0/0 route, curl https://ifconfig.me on the client prints the server's public IP.
WireGuard Mode
Pritunl can also serve WireGuard connections. The WireGuard packages must be installed on the server (the Ubuntu command above includes them). In the server's settings, enable WireGuard, set the Virtual WG Network to a network with the same CIDR size as the Virtual Network, and choose the WG Port (UDP). Clients keep the same address on both networks (WireGuard documentation).
WireGuard connections go through the Pritunl Client, which offers a choice of OpenVPN or WireGuard when both are configured.
Day-to-Day User Management
- Someone leaves or loses a device: disable or delete the user in the console. That removes their access without touching anyone else's profile.
- PINs: an optional per-user PIN that has to be entered when connecting.
- Single sign-on and secondary authentication: the security guide lists which provider combinations it recommends and which modes (Radius, unsupported SAML providers, Duo on its own) to avoid.
Back Up MongoDB
Pritunl keeps its whole configuration in MongoDB, so a lost or damaged database means rebuilding organizations, users and servers, and handing out new profiles. Take a dump before every upgrade and on a schedule. The mongodb-org package installs the database tools, including mongodump:
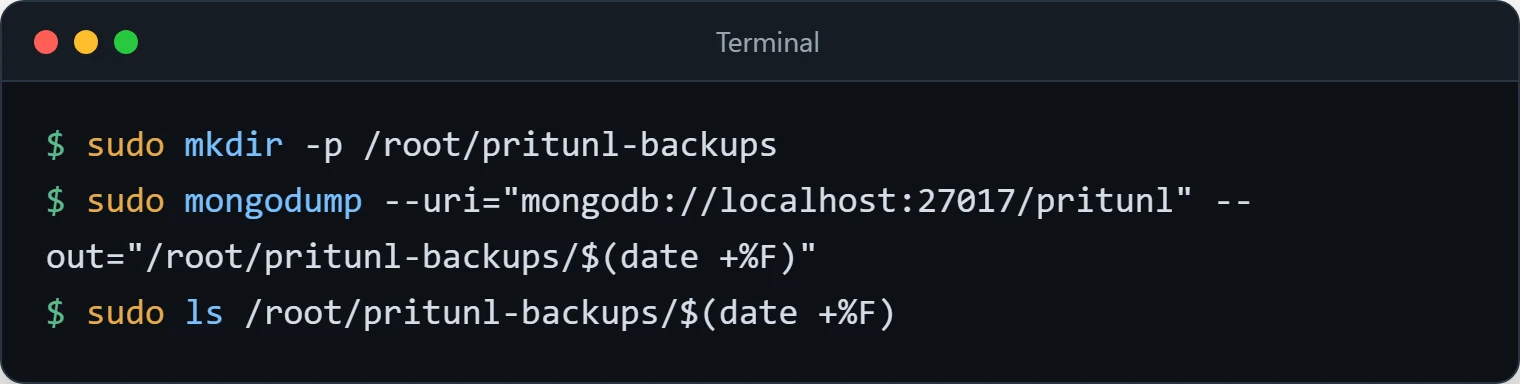
sudo mkdir -p /root/pritunl-backups
sudo mongodump --uri="mongodb://localhost:27017/pritunl" --out="/root/pritunl-backups/$(date +%F)"
sudo ls /root/pritunl-backups/$(date +%F)
The listing should contain a pritunl directory. The dump includes private keys for every user, so copy it off the server to encrypted storage. To restore on a fresh install, stop Pritunl first, then run sudo mongorestore --uri="mongodb://localhost:27017" --drop /root/pritunl-backups/DATE and start Pritunl again. A backup you've never restored is a guess, so try the restore once on a test VM. The security guide also recommends enabling password authentication on the database.
Updates
sudo apt update
sudo apt upgrade pritunl
sudo systemctl restart pritunl
According to Pritunl's security guide, the Pritunl service has to be restarted manually to complete an update, while its web server restarts on its own. Restarting drops connected VPN sessions briefly, so do it at a quiet time. The same guide recommends enabling automatic system updates.
When Something Doesn't Work
- Users get authentication errors after updating their client. The installation page notes that newer OpenVPN clients can send the password in an encoded format that older Pritunl servers don't recognise. Update the Pritunl package on the server.
- The console or VPN broke after enabling a firewall on the server. UFW, firewalld or extra iptables rules interfere with the rules Pritunl manages. Disable the software firewall and filter in the security group instead.
- Clients connect but can't reach other networks in the VPC. On AWS, the instance's source/destination check is still enabled; on Google Cloud, IP forwarding wasn't enabled for the instance.
- The Let's Encrypt certificate isn't issued or doesn't renew. The domain's DNS record must point at the server's public IP, and TCP 80 must be open to the internet. The certificate renews automatically only while both stay true.
- Connections fail under load. The configuration page recommends raising the open file limit on the Pritunl and MongoDB servers and shows the
limits.conflines for it. - The VPN server won't start. Check the server's output in the console and
sudo journalctl -u pritunl -b. A UDP port that another server or process already uses is a common cause.
Removing Pritunl
If this was a trial: delete the users and servers in the console, then remove the packages and repositories:
sudo systemctl disable --now pritunl mongod
sudo apt-get purge pritunl "mongodb-org*"
sudo rm /etc/apt/sources.list.d/pritunl.list /etc/apt/sources.list.d/mongodb-org.list /etc/apt/sources.list.d/openvpn.list
sudo apt update
Remove the VPN and console ports from the security group, delete any DNS record you created, and delete the VM if it existed only for this, so it stops costing money. Re-enable UFW (sudo ufw allow OpenSSH, then sudo ufw enable) if the server stays in use for something else.
Next Steps
- Lock down SSH on the host with Locking Down SSH.
- To see what Pritunl automates, build the same thing by hand with OpenVPN Cloud Deployment.
- If your users only need to reach a few machines, a mesh such as Tailscale avoids running a VPN gateway at all.