Versions: this guide follows the OPNsense 26.7 "Xenial Xenops" series; the newest update when it was revised was 26.7.7 (October 13, 2026), listed in the 26.7 release notes. According to the updates documentation, OPNsense publishes two major releases a year, named after the year and month (26.1 in January, 26.7 in July), with minor updates about every two weeks. 26.7 moved several pages to a new framework, so some menus differ from older guides; the differences that matter are noted where they come up.
Why Replace Your Router?
Consumer and ISP-supplied routers get updates only for as long as the vendor provides them, and they expose whatever settings the vendor chose. On OPNsense you write the firewall rules per interface and watch a live log of what each rule allowed or blocked. WireGuard, OpenVPN and IPsec are built in, as are VLANs, Suricata-based intrusion detection and traffic shaping. Updates follow the published schedule above rather than a vendor's support window.
Hardware Requirements
OPNsense needs at least two network interfaces (WAN and LAN). The hardware sizing page lists these specifications for running all standard features:
- Reasonable: 1 GHz dual-core CPU, 4 GB RAM, 40 GB SSD (the installer itself needs at least 3 GB of RAM).
- Recommended: 1.5 GHz multi-core CPU, 8 GB RAM, 120 GB SSD.
The same page notes that a caching proxy, a large captive portal or very many simultaneous connections need more resources, and that Intel network cards are reliable under FreeBSD. Hardware support is the same as FreeBSD's, so check the FreeBSD hardware notes for your NICs.
Dedicated Hardware
- Small fanless PCs with several NICs, sold as firewall appliances
- A desktop PC with an added dual-port Intel NIC
- Appliances from OPNsense partners, such as Deciso, the company behind the project, listed on the partner page
Virtual Machine
OPNsense also runs as a VM, for example on Proxmox VE (see the Proxmox VE Setup Guide). Give it the RAM and disk from the specifications above, and pass through physical NICs, or at least give WAN its own bridge, so the hypervisor host isn't exposed to the internet directly.
Not an option: Raspberry Pi
OPNsense publishes installation images for 64-bit x86 (amd64) only, so ARM boards such as the Raspberry Pi aren't supported. For a Pi-based access point, look at RaspAP instead.
Installation
Download and Write the Image
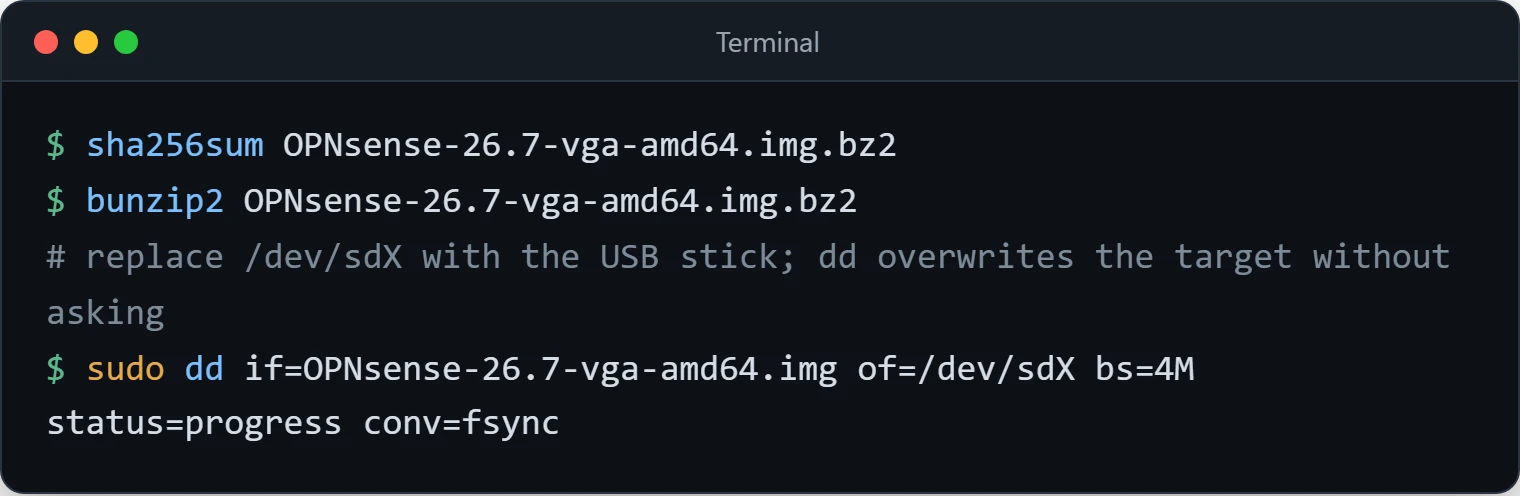
Download an image from opnsense.org/download. The installation guide describes the types: vga (USB image, VGA console), serial (USB image, serial console), dvd (ISO) and nano (preinstalled image for small drives). Verify the SHA-256 checksum against the value published in the release notes or the mirror's checksum file, decompress the .bz2 archive, and write the image to a USB stick with dd or an image writer. On Linux:
sha256sum OPNsense-26.7-vga-amd64.img.bz2
bunzip2 OPNsense-26.7-vga-amd64.img.bz2
# replace /dev/sdX with the USB stick; dd overwrites the target without asking
sudo dd if=OPNsense-26.7-vga-amd64.img of=/dev/sdX bs=4M status=progress conv=fsync
Check the device name with lsblk before running dd: pointing it at the wrong disk erases that disk.
Install Process
- Boot from the USB stick into the live environment.
- Log in as
installerwith the passwordopnsenseto start the installer. (Logging in asrootwith the same password gives you the live environment's console instead.) - Choose the target disk and file system, then follow the prompts to finish the installation.
- Reboot, remove the USB stick, and assign the interfaces from the console menu (WAN to the modem, LAN to your network).
- The LAN address defaults to 192.168.1.1; change it from the console menu if that clashes with your modem's network.
Initial Configuration
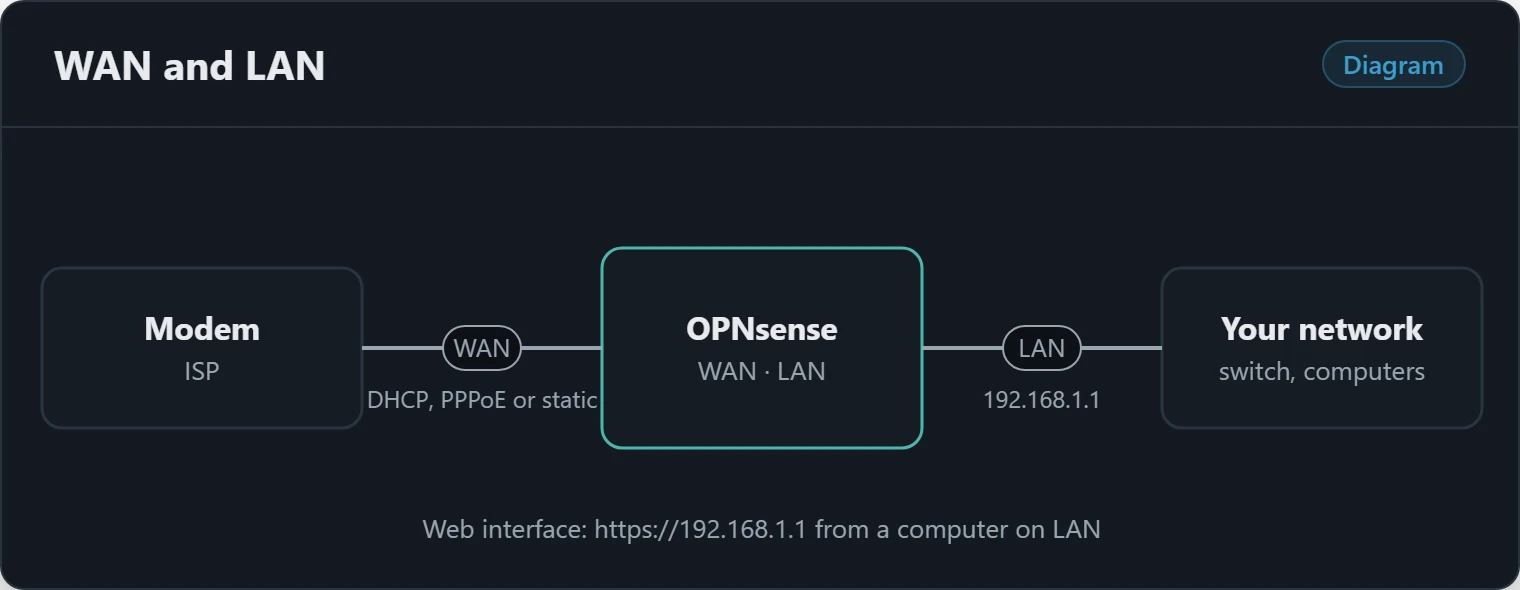
Connect a computer to the LAN port and open https://192.168.1.1. The documented default login is root / opnsense, unless you changed the password during installation or imported an existing configuration. Change it in the setup wizard. The browser warns about the self-signed certificate on first connection.
Setup Wizard
The wizard walks you through:
- General settings (hostname, domain, DNS servers)
- Time server
- WAN configuration (DHCP from the ISP, PPPoE or static)
- LAN configuration
- Changing the root password
Check: after the wizard, Interfaces → Overview shows an address on WAN, and a computer on LAN can open a website. Then run System → Firmware → Status once so the install from the 26.7 image picks up the current 26.7.x update.
Basic Firewall Rules
Start with the defaults, confirm that internet access works, and then add rules one at a time, testing each one. Changing many rules at once makes it hard to tell which one cut off your access to the web interface.
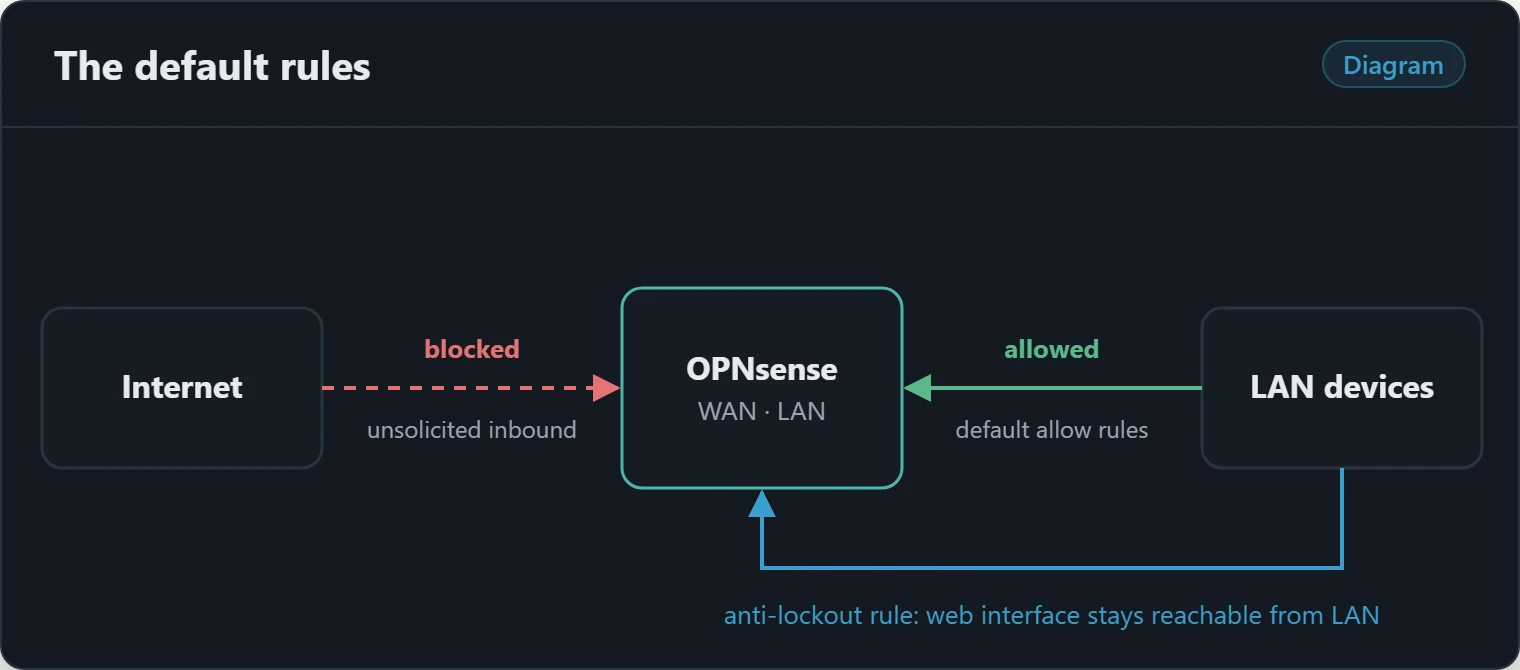
Out of the box:
- WAN blocks unsolicited incoming traffic.
- LAN has default allow rules, so devices can reach the internet. You can tighten these later.
- An automatic anti-lockout rule on LAN keeps the web interface reachable from the LAN side. Leave it in place until you've added and tested your own rule that allows management access.
Make rule changes from a computer on LAN, with a keyboard and screen (or the hypervisor console) attached to the firewall. If a change cuts you off, the console menu is the way back in (see Locked out of the web interface). Download a configuration backup (see Backup Configuration) before larger changes.
Creating Rules
Rules live under Firewall → Rules. In 26.7 the newer rules page is the default, and the old static per-interface pages moved to the optional os-firewall-legacy plugin. The release notes say existing rules keep working whether or not the plugin is installed, and a migration assistant moves them to the new page. Since 26.7.5 the old outbound NAT page is in the same plugin as well; its replacement is Firewall → NAT → Source NAT. Each rule has:
- Action: Pass, Block or Reject
- Interface: where the rule applies
- Direction: in or out (usually in)
- Protocol: TCP, UDP, ICMP or any
- Source and destination: addresses, networks or aliases
- Port: a single port, a range or an alias
Rules are evaluated top to bottom, and with Quick set (the default) the first match wins, so a broad block rule above a specific pass rule hides it. Changes take effect when you click Apply.
Check: Firewall → Log Files → Live View shows which rule matched each packet. Generate the traffic the rule is meant for and confirm the expected rule appears; it's the quickest way to debug a rule that doesn't behave as expected.
VLANs for Network Segmentation
VLANs keep groups of devices on separate networks, for example so IoT devices can't reach your computers. If subnets and gateways are new to you, Networking Fundamentals explains them first.
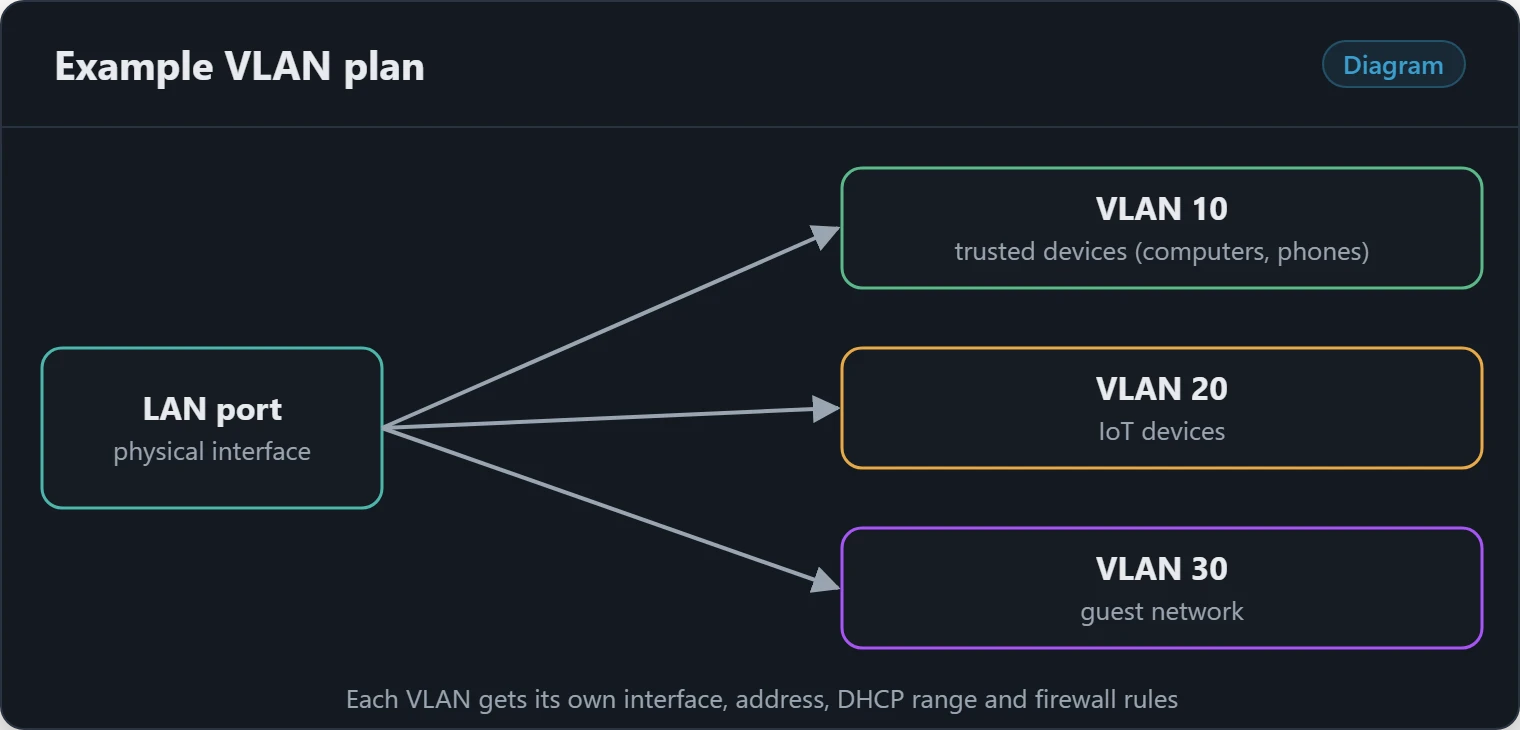
Example plan:
- VLAN 10: trusted devices (computers, phones)
- VLAN 20: IoT devices
- VLAN 30: guest network
- Create the VLAN devices under Interfaces → Devices (VLAN), on top of the physical LAN port.
- Assign each VLAN device under Interfaces → Assignments, enable it and give it a static address. Since 26.7.6 the interface settings sit in the assignments grid itself. The release notes point out that saving only queues the change: click Apply, because a reboot before applying discards it.
- Add a DHCP range for each VLAN (see DNS and DHCP below).
- Add firewall rules per VLAN interface; a new interface has no allow rules, so nothing passes until you add them.
Your switch and access points must carry the same VLAN tags on the right ports.
VPN Server
OPNsense includes WireGuard, OpenVPN and IPsec.
WireGuard Setup
The steps from the WireGuard how-to in outline:
- VPN → WireGuard → Instances: create an instance, generate its key pair with the cogwheel, and set a listen port (51820) and a tunnel address such as
10.10.10.1/24. The how-to warns against a /32 tunnel address and says to leave the instance's DNS field empty, because filling it overwrites OPNsense's own DNS settings. - VPN → WireGuard → Peers (or the Peer generator): add one peer per client device, with a single /32 address from the tunnel range as its Allowed IPs, then select the peers in the instance.
- VPN → WireGuard → General: enable WireGuard.
- Interfaces → Assignments: assign the WireGuard device (
wg1for the first instance) as an interface with no IP configuration. The how-to recommends this: it creates an alias for the tunnel subnet and an automatic source NAT rule, which clients need to reach the internet through the tunnel. - Add firewall rules: on WAN, pass UDP to the WAN address on the listen port; on the WireGuard interface, pass traffic from the tunnel subnet to whatever clients should reach.
- Add normalization rules that clamp the TCP MSS on the WireGuard group (1380 for IPv4 with the default 1420 MTU). The how-to explains that without them ping and UDP work, but some TCP connections through the tunnel stall.
Check: after a client connects, VPN → WireGuard → Status shows a recent handshake for its peer. The concepts (keys, peers, AllowedIPs) are the same as on Linux; WireGuard Cloud Deployment explains them and what to check when a client gets no handshake.
Intrusion Detection (Suricata)
Configure it under Services → Intrusion Detection → Administration. Suricata compares traffic against rule sets of known attack patterns. In IDS mode it only alerts; in IPS mode it can drop matching traffic, which uses netmap and needs a network card that netmap supports. The intrusion prevention docs explain the modes and settings. Inspection costs CPU, so measure your throughput after enabling it, especially on low-power hardware, and enable rule sets selectively.
DNS and DHCP
Unbound provides DNS. For DHCP, the DHCP documentation lists Dnsmasq as the default for DHCPv4, DHCPv6 and router advertisements, with Kea as an alternative for larger setups. ISC DHCP is end-of-life, so don't build a new setup on it.
Local DNS Entries
Under Services → Unbound DNS → Overrides, add host entries such as nas.home → 192.168.1.50.
DHCP Ranges and Reservations
With Dnsmasq, ranges are under Services → Dnsmasq DNS & DHCP → DHCP ranges, and fixed addresses for specific MAC addresses are under Services → Dnsmasq DNS & DHCP → Hosts.
Backup Configuration
Download the configuration under System → Configuration → Backups before every upgrade and after every significant change, and store a copy off the firewall. The whole configuration is one XML file, and the installation guide describes importing it while installing on new hardware. The file can contain password hashes and VPN private keys, so keep it somewhere private, or use the encryption option on the backup page.
Updates
Check for updates under System → Firmware → Status. Minor updates arrive about every two weeks within a series. Major upgrades (for example 26.1 to 26.7) are installed offline after a reboot, and the updates documentation recommends watching them from a VGA display or serial console. Leave the release type on "Production" unless you know you need development builds.
Read the release notes before a major upgrade. For 26.7 they warned that third-party repositories and plugins could interfere because the upgrade moved to FreeBSD 15.1 and OpenSSL 3.5, and that some Hyper-V guests could panic (26.7.6 fixed the Hyper-V panics but caused segmentation faults for some users, which 26.7.7 corrected, so Hyper-V guests should run 26.7.7 or later). On a VM, take a snapshot first; on hardware, download a configuration backup.
Troubleshooting
Locked out of the web interface
Use the console (keyboard and screen, serial, or the hypervisor console). The console menu has options to set an interface's IP address, reset the root password, restore an earlier configuration backup, and open a shell. If a firewall rule is the problem, pfctl -d in the shell turns the packet filter off until the rules are next reloaded, which gives you a window to fix the rule in the web interface. Use it from the LAN side only, because WAN is unfiltered while it's off.
LAN clients have no internet after setup
- Interfaces → Overview: WAN needs an address and a gateway. With PPPoE, recheck the credentials from your ISP.
- If your modem's LAN also uses 192.168.1.0/24, the two networks overlap; change the OPNsense LAN address from the console menu.
- Firewall → Log Files → Live View: look for blocked traffic from the LAN client to see which rule caught it.
- If ping to
1.1.1.1works from a client but names don't resolve, check Unbound under Services → Unbound DNS. Networking Fundamentals has a step-by-step order for separating routing from DNS problems.
Throughput dropped after enabling a feature
Intrusion prevention and traffic shaping run on the CPU. Turn the feature off, measure again, and re-enable it with fewer rule sets if the hardware can't keep up.
Before You Rely On It
- Delete test rules, aliases and WireGuard peers you no longer use, so the rule set only contains what you meant to allow.
- Add plugins one at a time; each one uses resources and adds something to debug.
- Keep a current configuration backup off the firewall, and apply security updates promptly: the firewall sits at the edge of your network.
OPNsense or pfSense?
Both are FreeBSD-based and use the pf packet filter, so the core firewalling works the same way. The differences are in the project around it:
- Release schedule: OPNsense publishes two major releases a year with minor updates about every two weeks. Check Netgate's pfSense documentation for its current release model.
- Interface and API: OPNsense has been moving its pages to a newer framework with an API; the 26.7 release continued that with the firewall rules and interface assignment pages.
- Plugins: both have a package system; check that the specific packages you rely on exist for the platform you choose.
- Support and hardware: Deciso backs OPNsense and Netgate backs pfSense, and both sell appliances and commercial support.
- Community material: pfSense has been around longer, so there are more third-party guides for it; make sure a guide matches the platform and version you run.
For a new install, either works; pick the one whose interface, release cadence and documentation suit you. If you already run one and it works, there's no urgent reason to switch. If you'd rather stay on Linux, Linux Router Setup builds the same functions by hand, and OpenWrt covers consumer router hardware.